


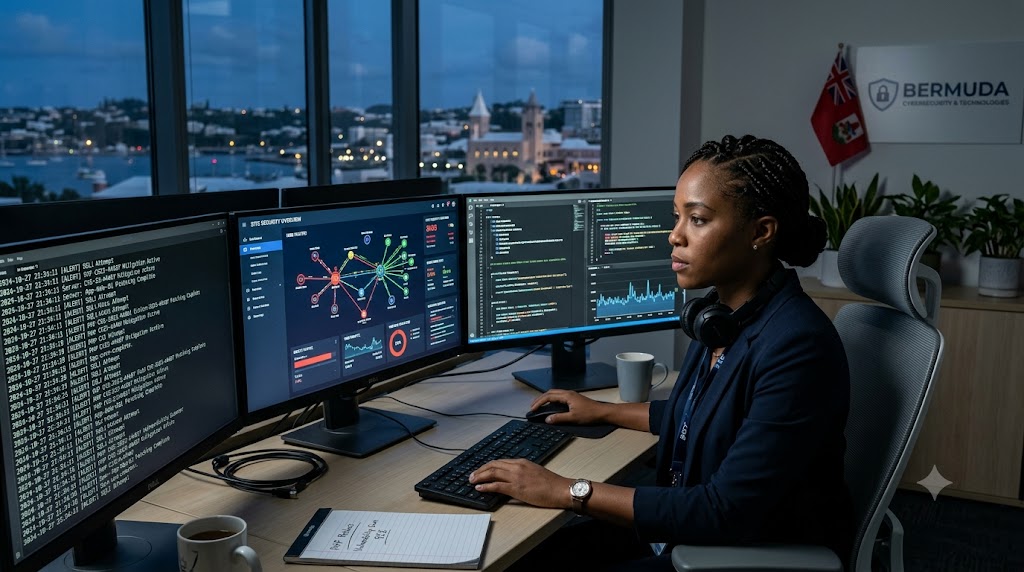
Bermuda businesses are being urged to check their websites and online systems for critical software vulnerabilities after cybersecurity experts warned that attackers could exploit affected PHP installations to take control of web servers.
The warning, reported by The Royal Gazette on October 23, concerns two vulnerabilities identified as CVE-2026-109618 and CVE-2026-109619. PHP is widely used to run website features and applications, including systems that businesses may rely on for customer accounts, online services and internal operations.
Bermuda cybersecurity specialist Mike Perkins of NorthRock CyberRisk and Compliance Ltd. said the vulnerabilities could allow commands to be executed on affected servers without an attacker needing to sign in. A compromised website could then potentially be misused to host fake login pages, steal passwords or distribute malicious downloads.
The risk may be especially difficult for smaller organisations to assess if they rely on an external developer or hosting company and are unsure who manages their software updates. Websites built with content-management systems such as WordPress may also rely on PHP behind the scenes.
Experts are advising organisations to confirm whether their systems use affected PHP versions, apply the relevant security fixes and verify that the updates are working. Where software is no longer supported, a more substantial upgrade may be necessary. Reviewing server logs and looking for unexpected changes can also help identify signs of earlier compromise.
The issue highlights the importance of maintaining an accurate inventory of website software, keeping systems supported and clarifying cybersecurity responsibilities between businesses and their service providers.
Bermuda organisations are being urged to treat software maintenance as an essential part of protecting customer data and online services, rather than waiting until a security incident occurs.
Comments (0)
Sign in to join the conversation.